Trusted by security and compliance teams at 100+ regulated companies in

MedTech
SAMD
AISaMD
FinTech
OT
Energy
eSports
Consumer SaaS
MedTech

Trusted by 100+ in

SiMD
SaMD
AISaMD
FinTech
OT
Energy
eSports
Consumer SaaS
SiMD

Trusted by 100+ security and compliance teams in

MedTech
SAMD
AISaMD
FinTech
OT
Energy
eSports
Consumer SaaS
MedTech

Audit-ready SBOM. With every build.

Interlynk generates SBOMs for everything you ship, from embedded C/C++ firmware to cloud services, and automates everything after: ingest, enrich, monitor, and share. Built for teams shipping under FDA 524B, EU CRA, NIS2, DORA, and PCI DSS 4.0.

Two business professionals reviewing cybersecurity data on a laptop, surrounded by security and compliance icons.

INDUSTRIES

INDUSTRIES

SBOM compliance for regulated industries.

SBOM compliance for regulated industries.

Healthcare

Financial Services

Government

Healthcare cybersecurity concept showing a professional interacting with secure medical data dashboards and encryption visuals.

FDA 524B SBOM

Medical device makers must now ship an SBOM with every premarket submission under FDA Section 524B, or risk a refuse-to-accept before review begins. Interlynk generates submission-ready SBOMs tied to the exact device build, tracks component vulnerabilities across the product lifecycle, and keeps your evidence audit-ready for FDA and global regulators.

Healthcare

Financial Services

Government

Healthcare cybersecurity concept showing a professional interacting with secure medical data dashboards and encryption visuals.

FDA 524B SBOM

Healthcare

Financial Services

Government

Healthcare cybersecurity concept showing a professional interacting with secure medical data dashboards and encryption visuals.

FDA 524B SBOM

Medical device makers must now ship an SBOM with every premarket submission under FDA Section 524B, or risk a refuse-to-accept before review begins. Interlynk generates submission-ready SBOMs tied to the exact device build, tracks component vulnerabilities across the product lifecycle, and keeps your evidence audit-ready for FDA and global regulators.

line background pattern

PLATFORM

PLATFORM

PLATFORM

The whole SBOM lifecycle. One platform.

Automated SBOM Management

Automate the creation and management of Software Bills of Materials (SBOMs) to ensure transparency, compliance, and faster response to vulnerabilities.

Open Source Management

Open Source Management

Gain full visibility and control over open-source components, licensing, and risks while streamlining compliance across your software supply chain.

Supplier Monitoring

Supplier Monitoring

Continuously track and assess third-party suppliers for security, compliance, and risk posture to strengthen your overall supply chain resilience.

Embedded SBOM Generator

Embedded SBOM Generator

Generate accurate SBOMs for embedded C/C++ firmware with lynkctl. IAR, GCC, or CMake build Supported.

Gain full visibility and control over open-source

components, licensing, and risks while streamlining compliance across your software supply chain.

COMPLIANCE

COMPLIANCE

COMPLIANCE

What the FDA expects, and how Interlynk delivers it.

What the FDA expects, and how Interlynk delivers it.

FDA cybersecurity requirements (524B)

Generate the SBOM artifacts FDA expects in premarket submissions — formatted, complete, and traceable to the device build that shipped.

FDA cybersecurity requirements (524B)

Generate the SBOM artifacts FDA expects in premarket submissions — formatted, complete, and traceable to the device build that shipped.

Vulnerability monitoring across the supply chain

Watch every component in every version for new CVEs as they're disclosed. Filter out what doesn't apply with VEX, so your team responds to real risk instead of triaging noise.

Vulnerability monitoring across the supply chain

Watch every component in every version for new CVEs as they're disclosed. Filter out what doesn't apply with VEX, so your team responds to real risk instead of triaging noise.

Demonstrating secure-by-design practices

Map your SDLC artifacts to FDA's secure-by-design expectations automatically — version control, dependency review, vulnerability response — without rebuilding the evidence trail for every submission.

Demonstrating secure-by-design practices

Map your SDLC artifacts to FDA's secure-by-design expectations automatically — version control, dependency review, vulnerability response — without rebuilding the evidence trail for every submission.

SBOM mandates and documentation gaps

Close the gap between what your dev team builds and what your regulatory team needs to submit. Interlynk reconciles the two automatically, so nothing gets lost between sprints and submissions.

SBOM mandates and documentation gaps

Close the gap between what your dev team builds and what your regulatory team needs to submit. Interlynk reconciles the two automatically, so nothing gets lost between sprints and submissions.

Managing patch & update expectations

Show FDA your patch posture across the device fleet at any point in time. Prioritize fixes by exploitability, not CVSS alone.

Managing patch & update expectations

Show FDA your patch posture across the device fleet at any point in time. Prioritize fixes by exploitability, not CVSS alone.

Audit & submission readiness

One queryable record per device, one click to export. Stop assembling submission packages from spreadsheets the night before they're due.

Audit & submission readiness

One queryable record per device, one click to export. Stop assembling submission packages from spreadsheets the night before they're due.

FAQ

FAQ

FAQ

FAQ

FAQ

What is Interlynk?

Interlynk is an SBOM platform for companies that ship regulated software and devices. It generates SBOMs, including for embedded C/C++ firmware where most tools fail, and automates everything after: ingesting supplier SBOMs, enriching them, monitoring for new vulnerabilities, and sharing them with customers and regulators. More than 100 regulated companies across medical devices, industrial and energy, and financial services use Interlynk to meet FDA 524B, EU CRA, and similar requirements.
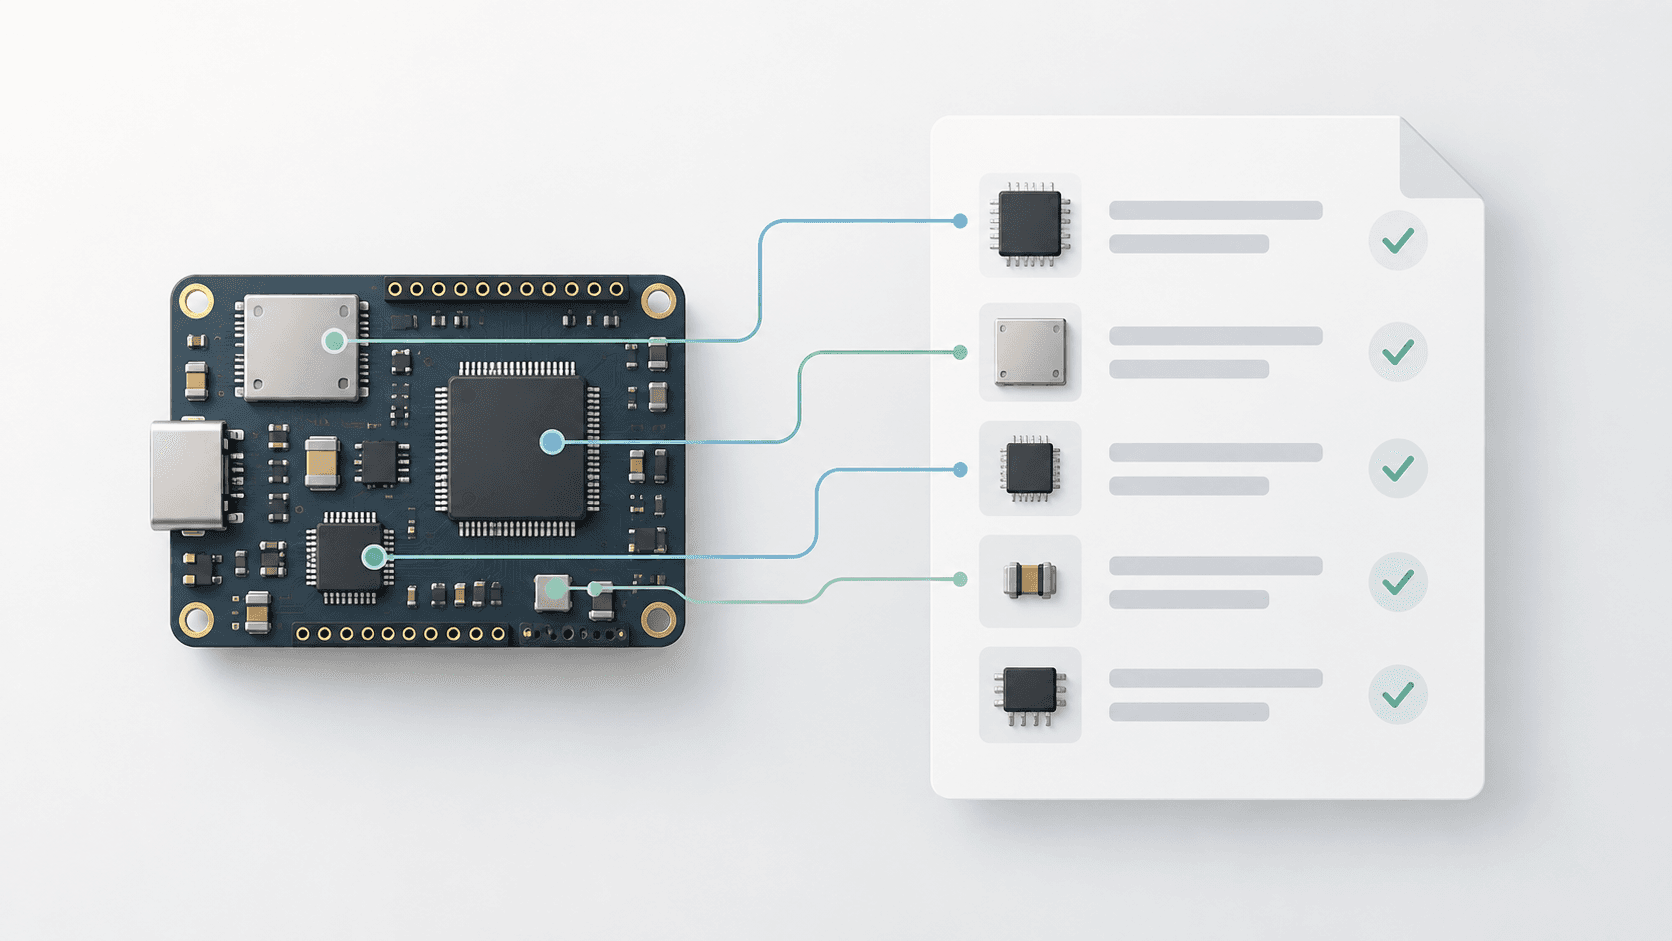
Can Interlynk generate SBOMs for embedded C/C++ firmware?

Which toolchains and microcontrollers does Interlynk support?

How is Interlynk different from Syft, Trivy, and other open source SBOM generators?

How is build-time SBOM generation different from binary analysis?

Does Interlynk help with FDA 524B and EU CRA SBOM requirements?

Does Interlynk work in air-gapped or offline environments?

Which vulnerability sources does Interlynk use?

Can I generate SBOMs automatically in CI?

Trusted by security and compliance teams at 100+ regulated companies

Audit-ready SBOM. With every build.

Interlynk automates SBOMs, manages open source risks, monitors suppliers, and prepares you for the post-quantum era, all in one trusted platform.

Trusted by security and compliance teams at 100+ regulated companies

Interlynk automates SBOMs, manages open source risks, monitors suppliers, and prepares you for the post-quantum era, all in one trusted platform.

Audit-ready SBOM. With every build.

Trusted by security and compliance teams at 100+ regulated companies

Interlynk automates SBOMs, manages open source risks, monitors suppliers, and prepares you for the post-quantum era, all in one trusted platform.

Audit-ready SBOM. With every build.