NEW: Build Arm / Keil SBOM with lynkctl
Features
Solutions
Resources
Company
Book Demo
Signup
Blog
Nov 4, 2026
An SBOM is not a malware scanner and does not prove a binary is clean. Here is how software inventory helps you scope a supply-chain attack, and why coverage and artifact traceability decide whether it helps.
Oct 27, 2026
Receiving an SBOM is not the same as trustworthy software transparency. Here are the three levels of SBOM trust, five checks for a supplier SBOM, and how to score quality with sbomqs without overstating what a score proves.
Oct 22, 2026
PHP2Shell explained: what CVE-2026-109618 and CVE-2026-109619 are, how two PHP engine memory-safety flaws enable unauthenticated RCE and memory disclosure, how the coordinated disclosure fell apart, affected and fixed versions, and how to respond.
Oct 20, 2026
The CRA's harmonised standards are running late and none is cited in the Official Journal yet. Here is what the delay changes, what it does not, and why your SBOM and vulnerability-handling work should continue now.
Oct 13, 2026
What VEX is, the four status values, the format landscape (CSAF, OpenVEX, CycloneDX, SPDX 3.0), and how to operationalize VEX to reduce SBOM vulnerability noise and support CRA and FDA reporting.
Oct 8, 2026
The Linux Foundation's OpenChain Automotive SBOM Framework 1.0 defines a common set of information for automotive supplier handoffs. Here is what the framework requires, what it leaves open, and why accurate generation still matters.
Sep 30, 2026
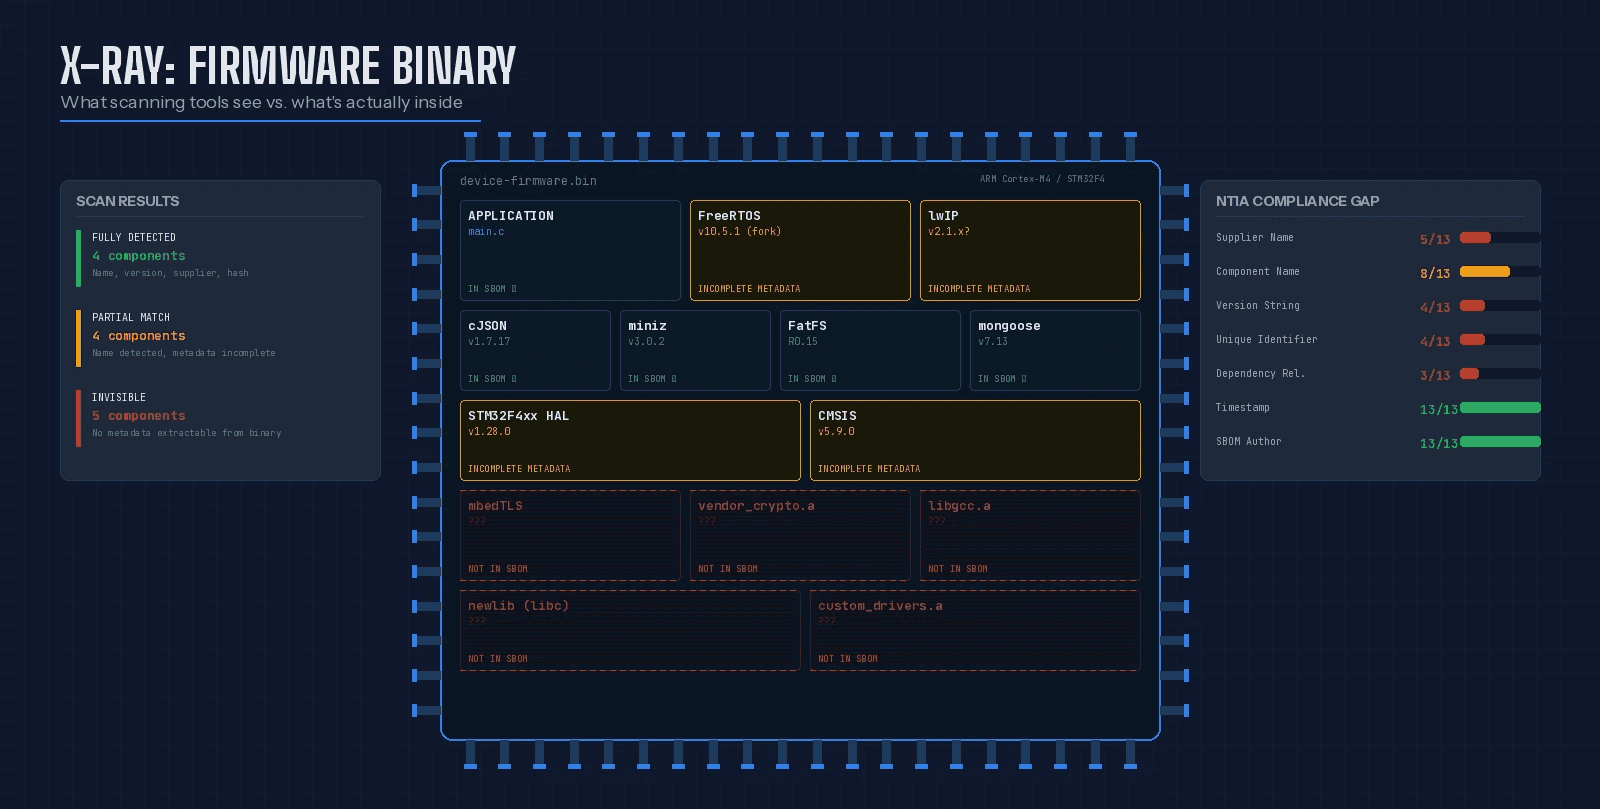
Why firmware SBOMs disagree: source scanning sees what is present, binary analysis sees the image but infers identity, and build-aware generation reads the real build. How to tell which is accurate and prove what actually shipped.
Sep 29, 2026
CMake added experimental native SBOM generation in a 2026 release (SPDX 3.0.1, DARPA-funded). Here is how to turn it on, exactly what it records, and where it still needs a build-aware layer for embedded firmware.
Sep 27, 2026
How to generate an SBOM from a CMake build in 2026 - CMake's new native SBOM support, open-source modules, binary analysis, and build-aware generation compared, with what each one captures and misses.
Sep 26, 2026
A vendor-neutral comparison of the best SBOM tools in 2026 across generation, management, and compliance, with side-by-side tables to match each tool to your use case.
Sep 25, 2026
We generated an SBOM for Meta's MUSE AI-agent VM and ran a vulnerability review in Interlynk: 279 findings, 14 critical. Here's how to inspect your own.
Sep 19, 2026
Lessons from 50+ embedded SBOM proofs of concept, with practical guidelines for engineers evaluating commercial and open-source SBOM generators.
Sep 10, 2026
A cryptographic bill of materials (CBOM) inventories the algorithms, keys, and certificates in your software, and supports post-quantum migration readiness.
Aug 28, 2026
The CRA's vulnerability reporting starts 11 September 2026: a 24-hour early warning, 72-hour notification, and 14-day or one-month final report. What to file, when, and where.
Aug 20, 2026
CISA's 2026 SBOM Minimum Elements raise the baseline, but compliance alone does not make an SBOM useful. The four tests that determine SBOM quality.
Aug 12, 2026
FDA 524B SBOM requirements for medical devices under Section 524B: what a cyber device is, refuse-to-accept rules, what the SBOM must contain, and postmarket duties.
Jul 16, 2026
A practical Q&A on generating accurate SBOMs for embedded C/C++ and IoT firmware, including STM32, NXP, Nordic, RTOS, binary blobs, linker maps, variants, and the EU Cyber Resilience Act.
Jul 15, 2026
How to generate a CycloneDX SBOM with cdxgen: install, per-language commands, GitHub Actions and Azure CI, evidence, signing, and depth pitfalls.
Jul 5, 2026
Generating accurate CycloneDX SBOMs for a Trusted Firmware-M build on STM32H5 using lynkctl — driven by the CMake build and linker maps, not source scanning
Jun 30, 2026
Enterprise SBOM management breaks at scale for five predictable reasons. Why generating SBOMs is the easy part, and managing them is where programs fail.
Jun 23, 2026
CycloneDX vs SPDX compared side by side: current versions, ISO and ECMA certification, tooling support, and which SBOM format fits your compliance needs.
Jun 20, 2026
CRA SBOM requirements, explained: what the EU Cyber Resilience Act and BSI TR-03183 mandate for your SBOMs, from data fields and formats to September 2026.
Jun 3, 2026
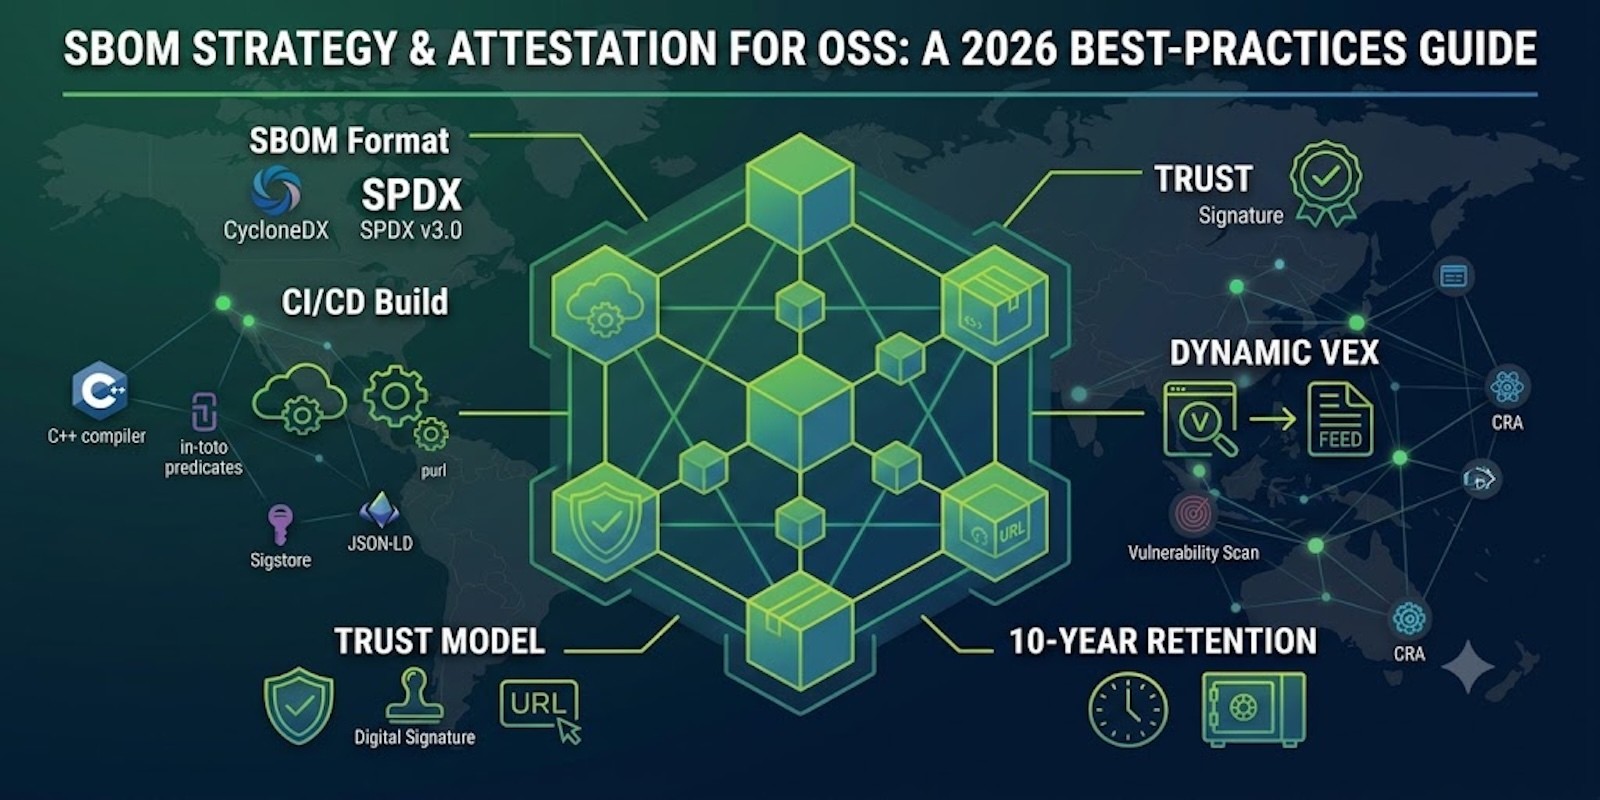
How open-source projects build an SBOM strategy and attestation model: formats, CI automation, signing, VEX, and CRA/FDA/NIS2 mapping. 2024-2026 best practices.
May 30, 2026
Your SCA tool already builds an SBOM, then locks it in a console. A practical guide to migrating to an open, SBOM-first workflow with no coverage gap.
May 25, 2026
Recent quantum computing breakthroughs have moved the PQC deadline earlier. What financial services, critical infrastructure, and medical device leaders need to do now.
May 8, 2026
A breakdown of MITRE's 2026 medical device cybersecurity findings: the biggest gaps in device security programs and what manufacturers should fix first.
Apr 17, 2026
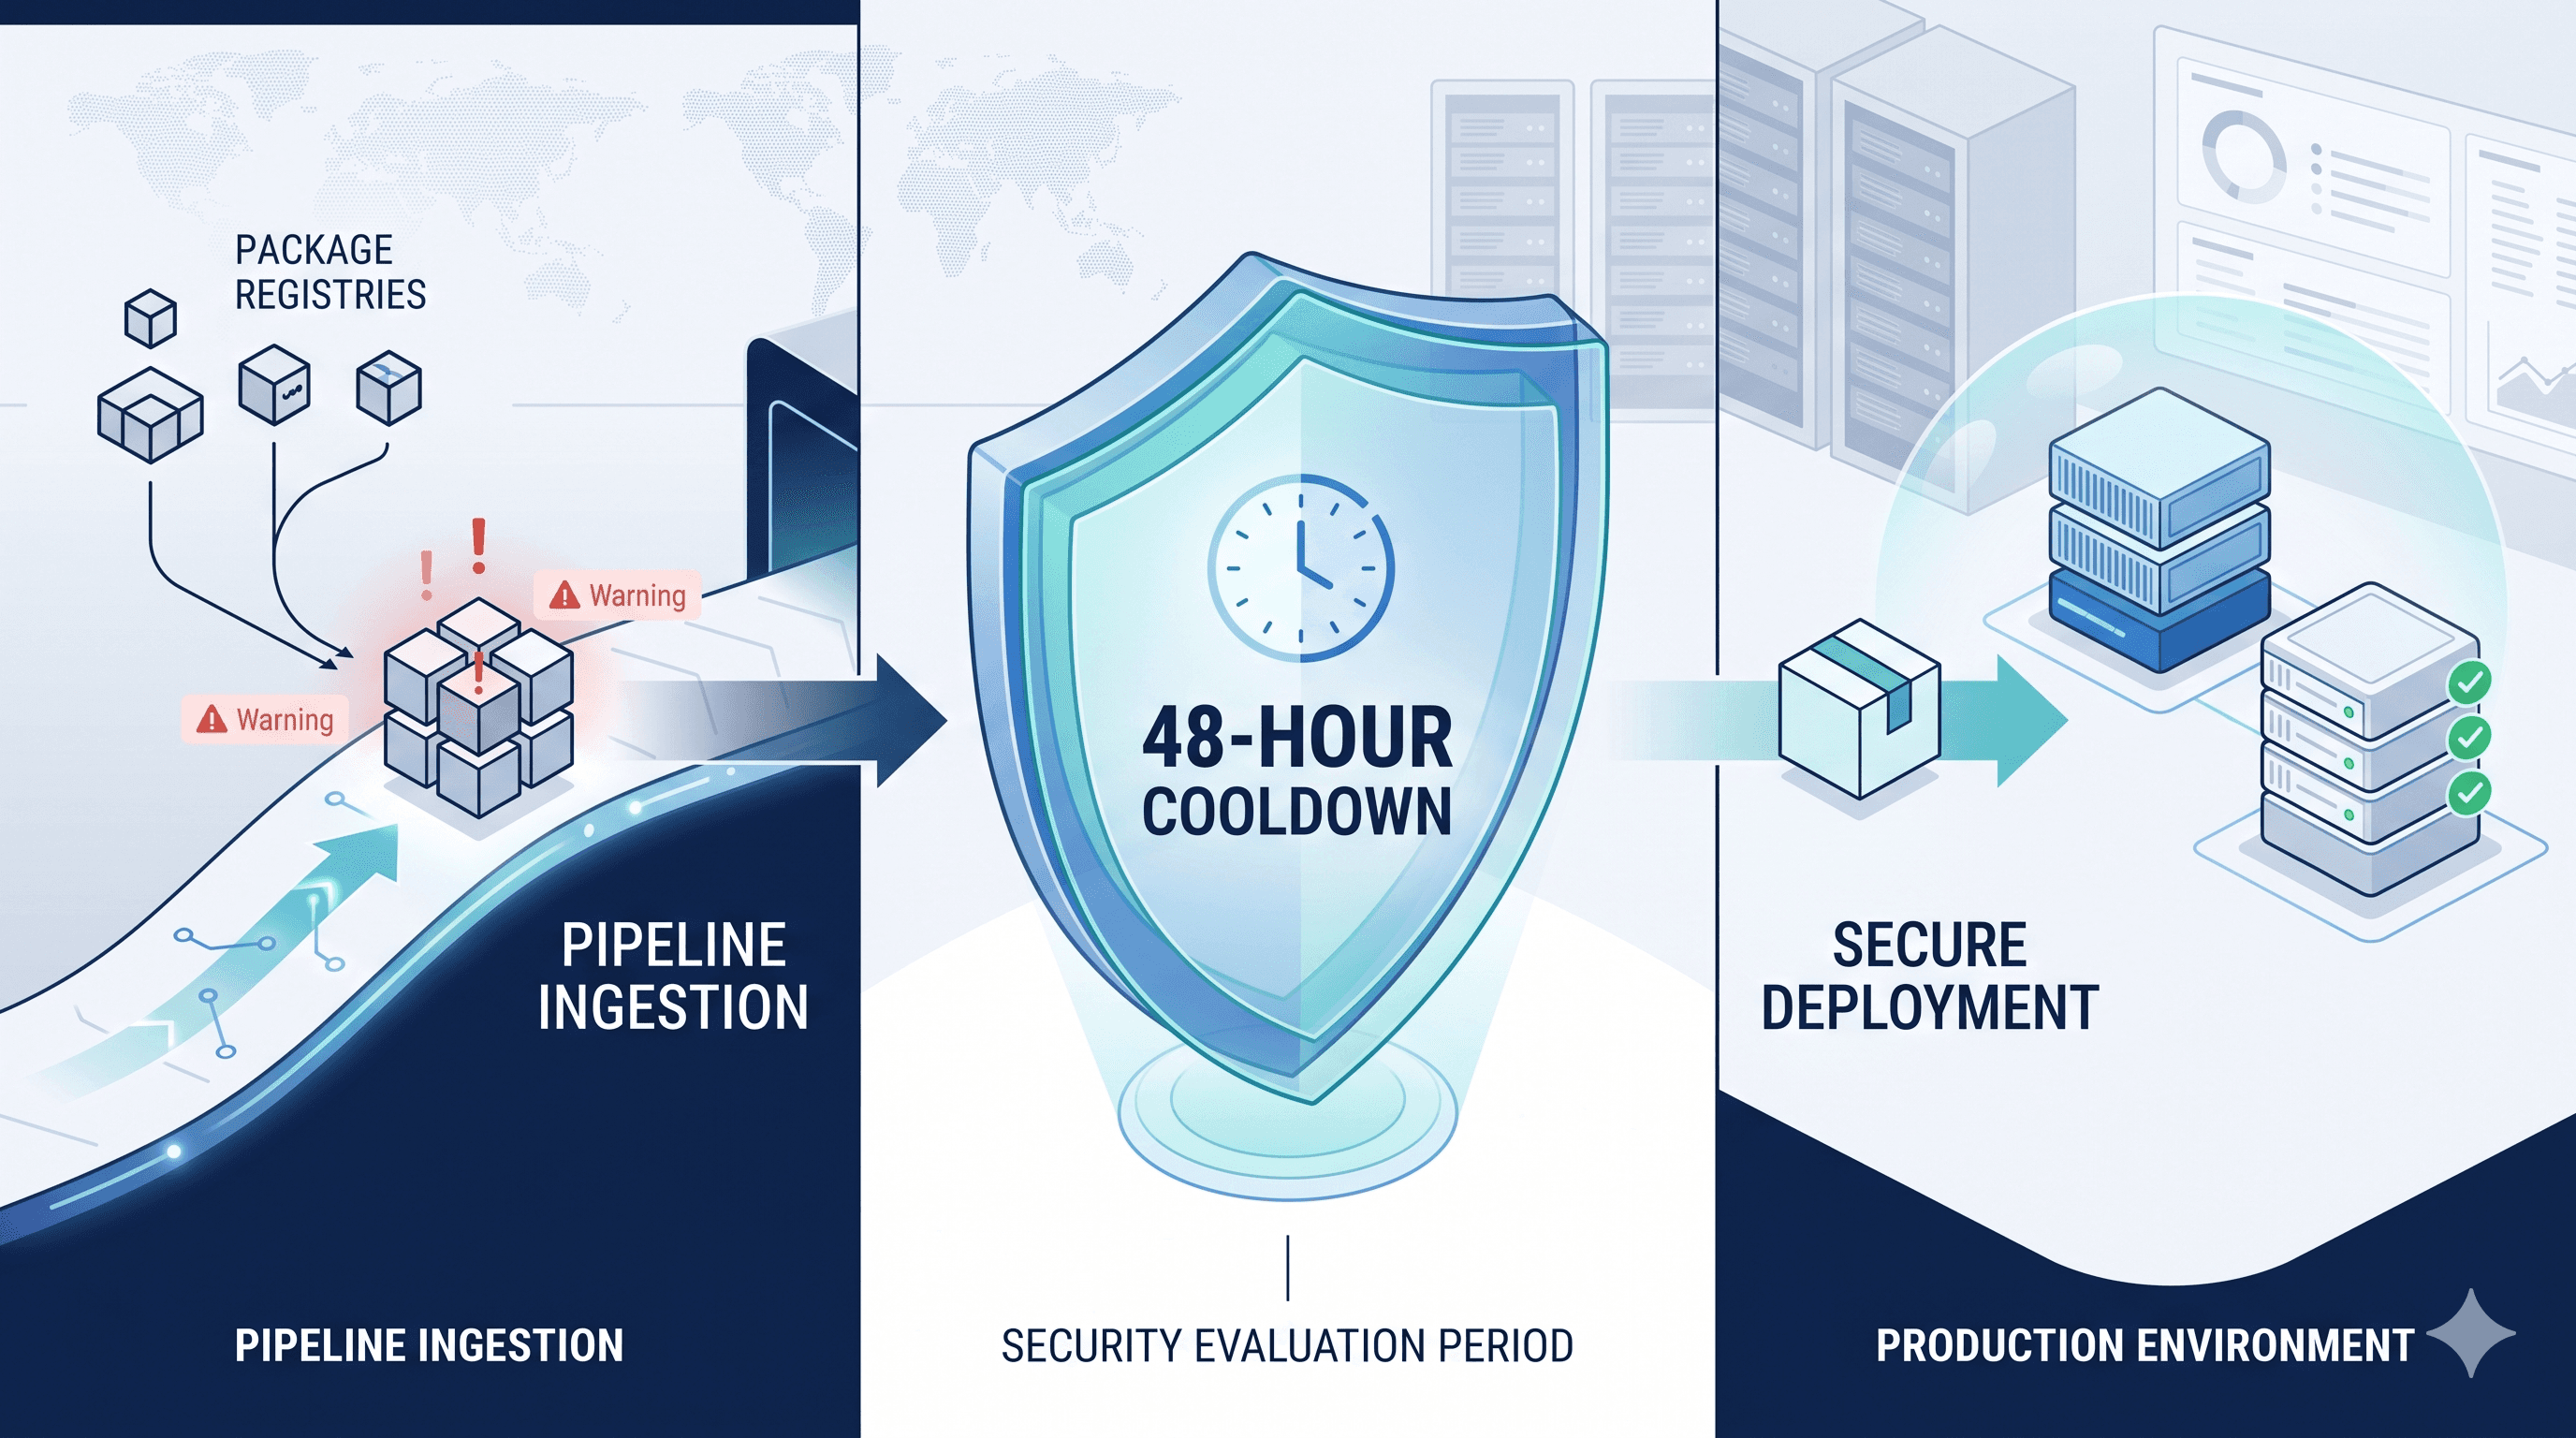
After the 2025 chalk/debug npm compromise, "cooldowns" delay adopting brand-new package versions. How SBOMs let you enforce and monitor dependency cooldowns.
Apr 9, 2026
Why SBOM generation for C/C++ is hard: vendored code, static linking, and build systems like CMake and Conan break most tools. The 2026 state of the art.
Apr 8, 2026
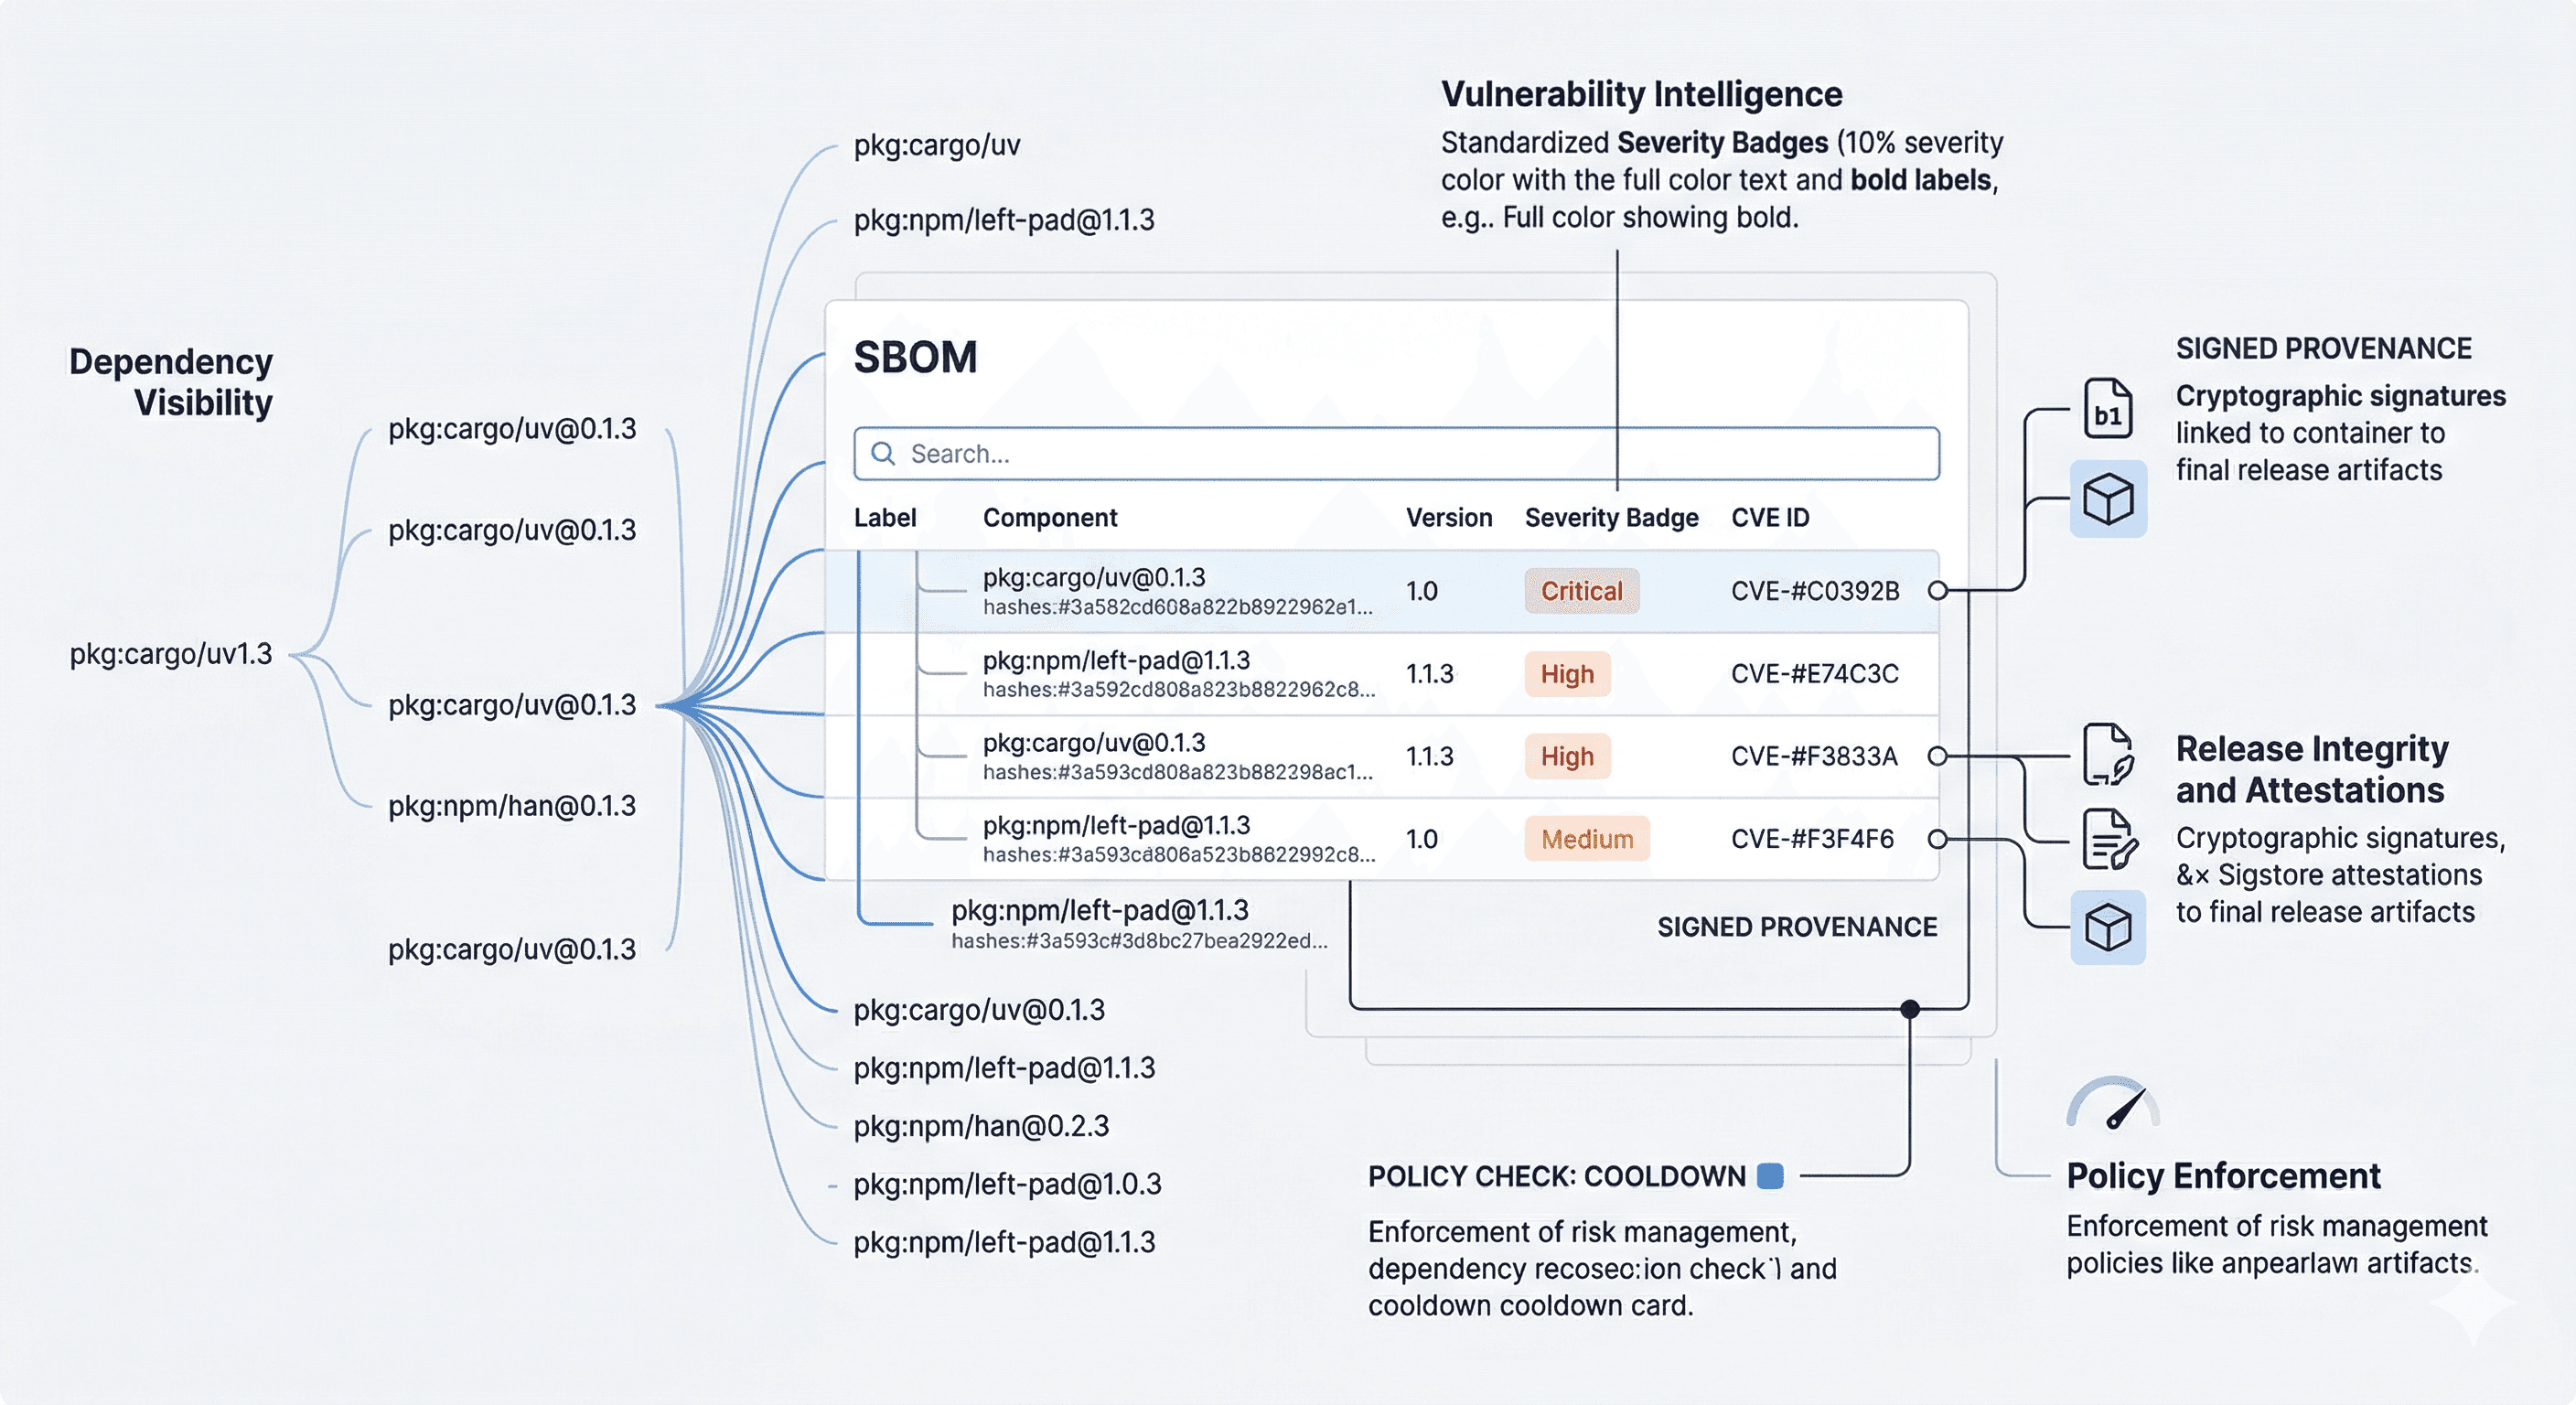
What Astral's security playbook reveals about SBOMs — practical lessons any software team can apply to strengthen supply-chain security and transparency.
Apr 5, 2026
How a 100-million-download npm package became the latest victim of an accelerating software supply chain playbook - and what to do about it.
Feb 14, 2026
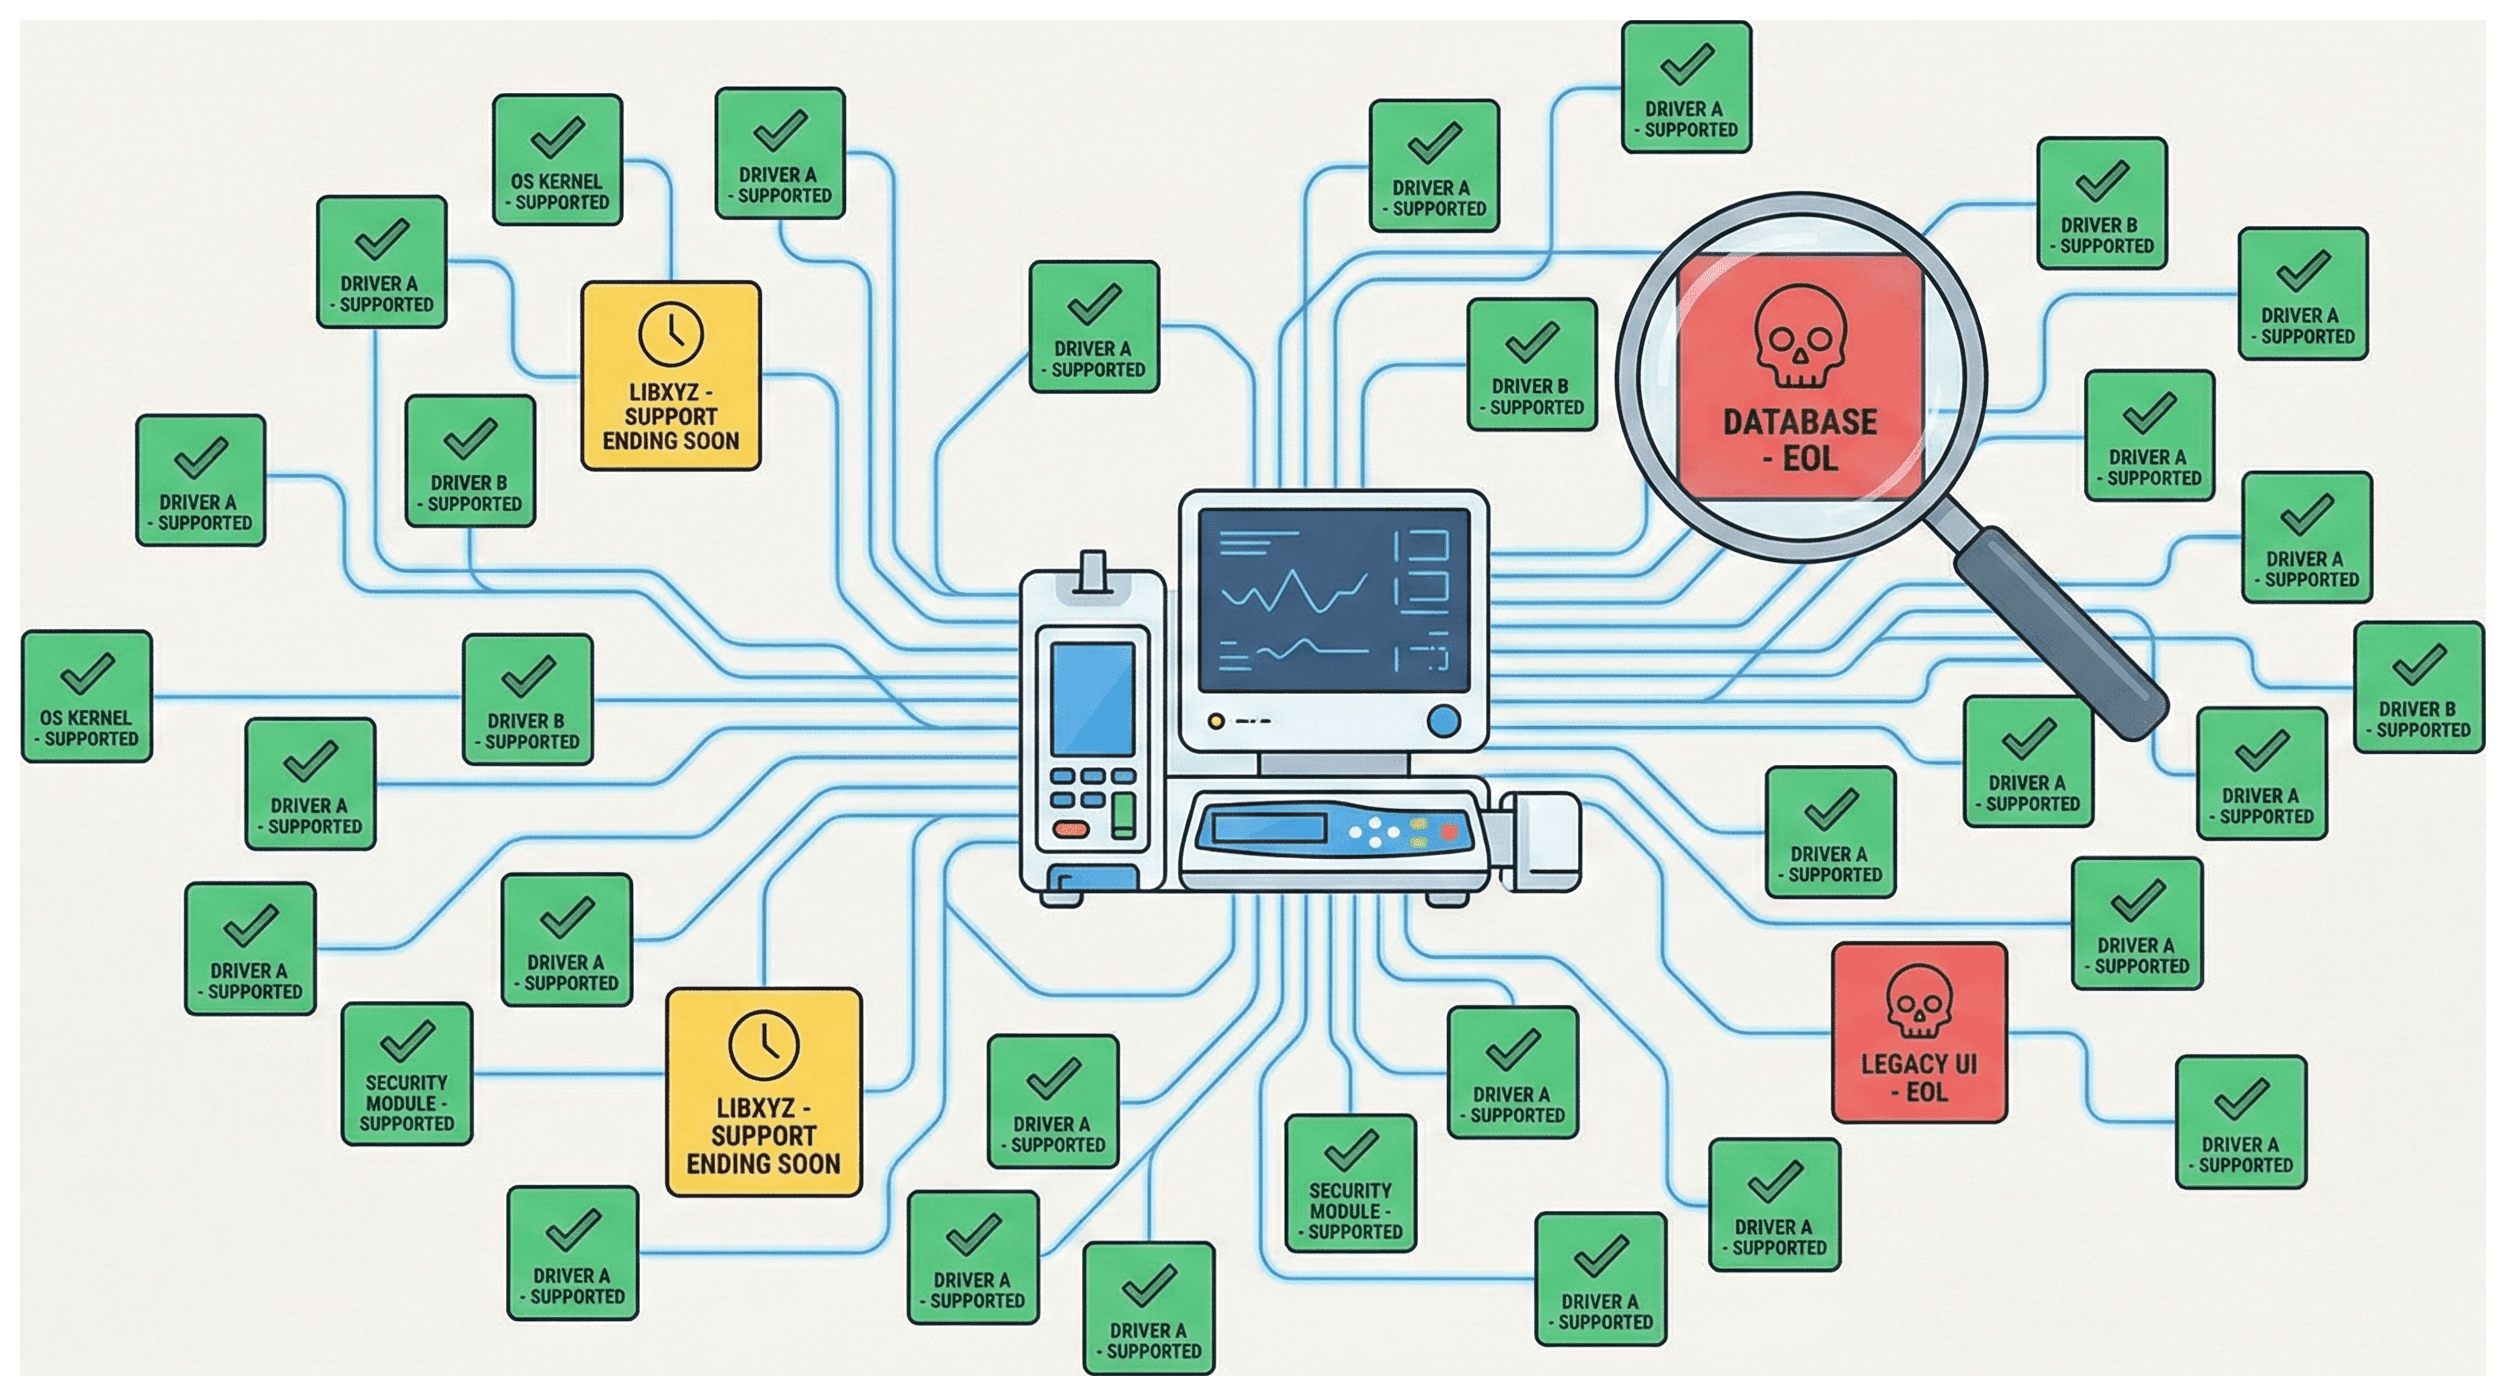
The FDA now requires software support status in medical device SBOMs. Learn what this means for manufacturers and how to demonstrate ongoing support compliance.
Jan 24, 2026
Introducing Lynk MCP: a conversational interface to query your software supply chain data. Ask questions about SBOMs, vulnerabilities, and compliance naturally.
Jun 17, 2025
What OTS, SOUP, and COTS software mean for medical devices, what FDA 524B and IEC 62304 require, and how to document third-party code in your SBOM.
Mar 23, 2025
Publishing SBOMs to GitHub Releases isn't enough — they go stale fast. Why static release SBOMs fail and how continuous SBOM management keeps them current.
Nov 19, 2024
The updated EU Product Liability Directive treats software as a product. How SBOMs help manufacturers manage defect liability and prove due diligence.
Nov 11, 2024
Technical guidance on SBOM adoption in India. Learn about emerging regulatory requirements and best practices for software supply chain transparency.
Oct 30, 2024
What's new in CISA's third-edition SBOM Framing Document — updated minimum elements and guidance shaping how organizations produce and consume SBOMs.
Oct 2, 2024
How to upload files to a GraphQL endpoint using Hurl. Step-by-step technical tutorial with code examples for API testing and file upload automation.
Sep 10, 2024
Interlynk launches a free tier for its SBOM automation platform. Get started with SBOM management, quality scoring, and vulnerability scanning at no cost.
Sep 6, 2024
How SBOMs underpin EO 14028, EU CRA, FDA, NIS2, DORA, and PCI DSS compliance — one software inventory mapped to every major cybersecurity mandate.
Aug 6, 2024
Biotronik selects Interlynk to support FDA cybersecurity compliance for its medical devices with automated SBOM management and vulnerability analysis.
Jul 27, 2024
How SBOMs help you meet the EU NIS2 Directive — what NIS2 requires for supply-chain security and why a software bill of materials is central to compliance.
Jul 10, 2024
Interlynk partners with Tumeryk to bring AI transparency and security through SBOM and software supply chain visibility for AI/ML applications.
Jun 16, 2024
How SBOMs support PCI DSS 4.0: use a software bill of materials to inventory components, track vulnerabilities, and meet payment-security requirements.
Jun 10, 2024
Analysis of the OpenChain Telco SBOM Guide. Key takeaways for telecommunications operators managing complex software supply chains and SBOM programs.
May 1, 2024
Everything about CycloneDX 1.6: new features, improvements, and what the latest SBOM standard version means for your software supply chain security program.
Apr 13, 2024
Five critical lessons from the XZ Utils backdoor incident. How SBOM and software supply chain security practices could help prevent similar attacks.
Mar 27, 2024
A guide to the CISA Secure Software Development Attestation Form (formerly M-22-18) — what federal software suppliers must attest to, and how SBOMs help.
Feb 22, 2024
SBOM in action: analyzing Ivanti Pulse firmware. A real-world case study showing how SBOM reveals hidden components and vulnerabilities in network devices.
Feb 1, 2024
How to assemble product-level SBOMs for a group of products using sbomasm. Best practices for aggregating, merging, and distributing composite SBOMs.
Jan 26, 2024
Five key insights from the latest SBOM adoption research. Data on industry trends, adoption rates, challenges, and best practices for SBOM implementation.
Jan 15, 2024
The 5 most common SBOM problems — incomplete components, weak metadata, version drift, format issues, and stale data — plus how to fix each one.
Dec 15, 2023
How to comply with NSA SBOM recommendations. Practical guidance on meeting national security requirements for software supply chain transparency.
Dec 11, 2023
A practical guide to CISA's minimum requirements for VEX: the required data fields, status justifications, and how to generate and share VEX at scale.
Oct 11, 2023
Federal Acquisition Regulation cyber compliance proposal: requirements, implications, and how SBOM helps contractors meet federal cybersecurity mandates.
Sep 3, 2023
SEC cybersecurity disclosure requirements explained. How public companies can use SBOM and software transparency to strengthen incident reporting processes.
Aug 31, 2023
Everything about SPDX 3.0: new features, profile model, improvements over SPDX 2.3, and what the latest version means for your SBOM and compliance workflow.
Aug 30, 2023
Frequently asked questions about SBOM compliance. Covers regulations, formats, implementation, tools, and best practices for software supply chain security.
Jul 16, 2023
How to use sbomasm for SBOM assembly in software products. Open source tool for merging, editing, and distributing Software Bills of Materials.
Jul 14, 2023
What the White House National Cybersecurity Strategy Implementation Plan means for software makers — key initiatives, timelines, and the growing role of SBOMs.
Jul 9, 2023
Everything about CycloneDX 1.5: new features, attestation support, and how this SBOM standard version advances software supply chain security practices.
Jul 3, 2023
Why your organization needs SBOM, part 2: regulatory drivers, supply chain attacks, and the business case for software transparency and risk management.
Jun 29, 2023
How to handle open source licenses in SBOMs. Guide to license identification, compliance tracking, and risk assessment for open source components.
Jun 26, 2023
Understanding VDR, VEX, OpenVEX, and CSAF: a guide to vulnerability disclosure formats and how they complement SBOM for supply chain security.
Jun 22, 2023
Guide to self-attestation for OMB Memorandum M-22-18. How software producers can meet federal secure development requirements and SBOM mandates.
Jun 18, 2023
Key updates from SBOM-a-Rama 2023. Summary of industry discussions, CISA guidance, tooling developments, and the future of SBOM adoption.
Mar 1, 2023
Why your organization needs SBOM, part 1: understanding software supply chain risks, visibility gaps, and how SBOMs provide transparency for security.
Dec 23, 2022
A roadmap towards cybersecure medical devices. How SBOM, FDA guidance, and supply chain security practices protect connected healthcare technology.
Dec 15, 2022
Why software disclosures matter for security and compliance. The growing demand for transparency in software supply chains and how SBOM enables it.
Trusted by security and compliance teams at 100+ regulated companies
Interlynk automates SBOMs, manages open source risks, monitors suppliers, and prepares you for the post-quantum era, all in one trusted platform.
SBOM Automation
Open Source Management
Supplier Monitoring
Post-Quantum Readiness
LynkMCP
FDA 524B Compliance
CRA Compliance
Embedded C/C++ SBOM
Windows Driver SBOM
Guides
News
Docs
Open Source Tools
Comparisons
References
About Us
Contact
Privacy Policy