






IN SHORT
OVERVIEW
EURO 15M
Maximum fines for non-compliance
24 Hours
10 Years
90%
TIMELINE
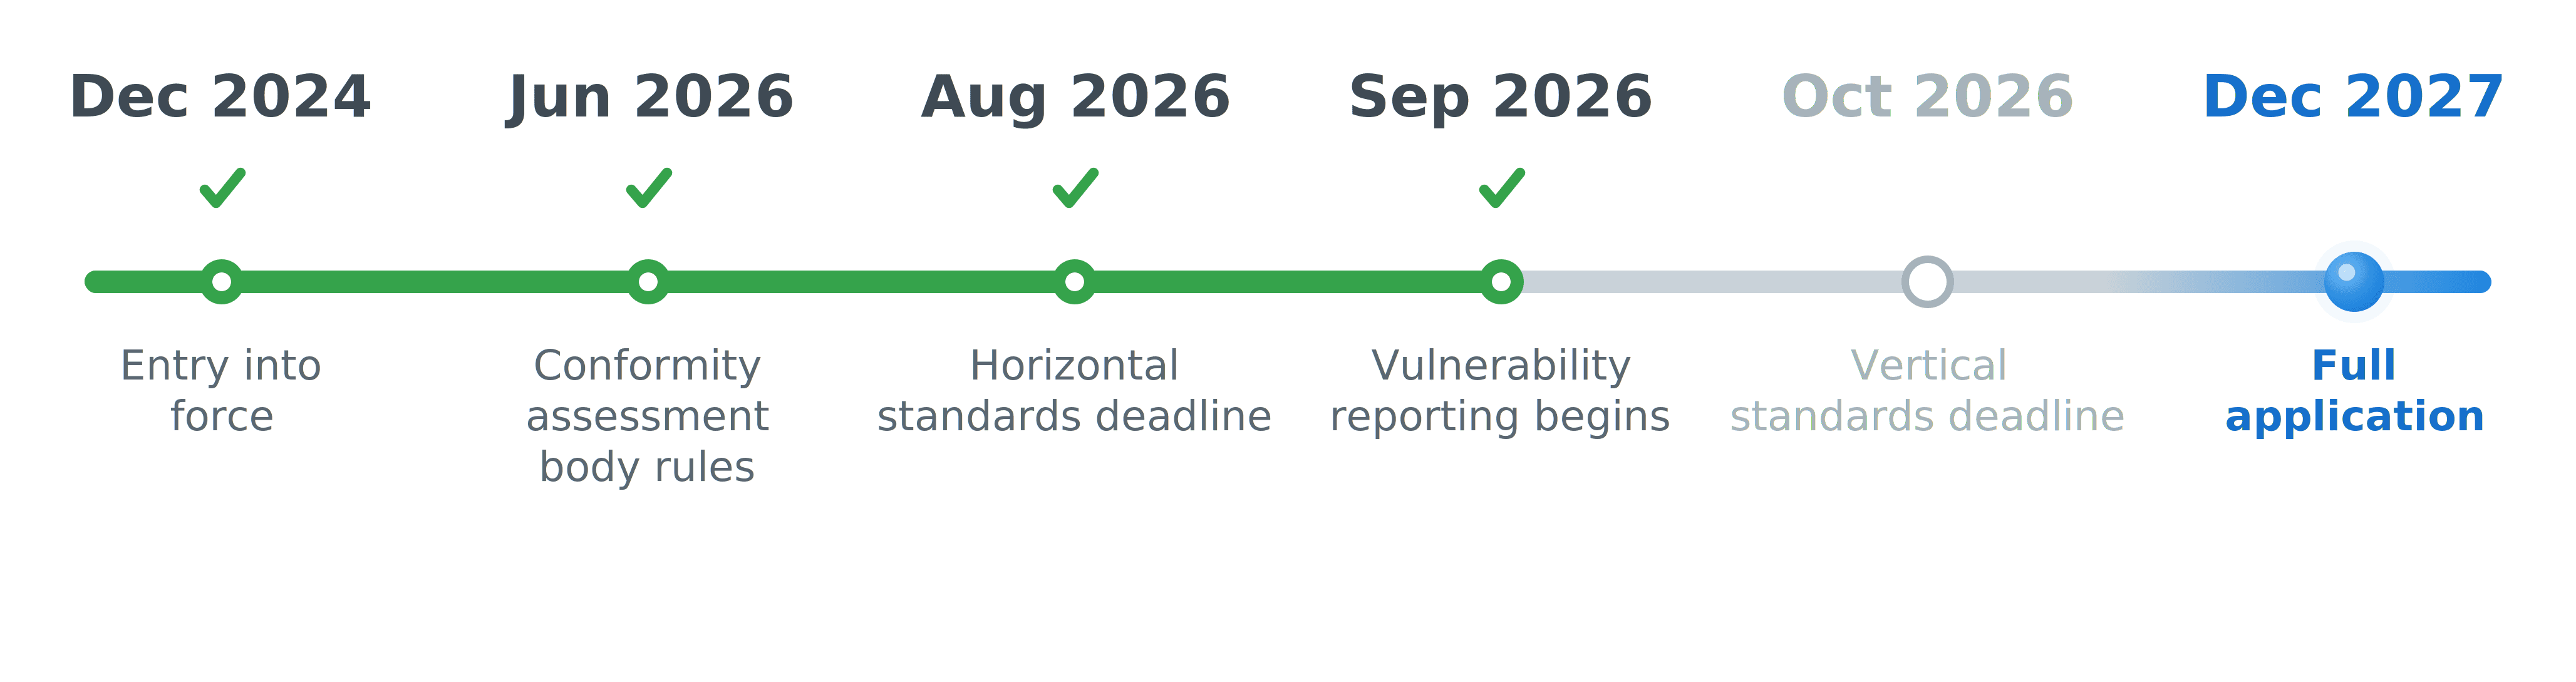
10 December 2024
Entry into force
Regulation takes effect. No manufacturer obligations yet.
11 June 2026
Conformity assessment body rules
Member States designate national authorities and notified bodies. No direct manufacturer duty.
August 2026
Horizontal standards deadline
Harmonised standards covering requirements common to all products with digital elements.
11 September 2026
Vulnerability reporting begins
24-hour early warning, 72-hour notification, 14-day final report. Applies to products already on the market.
October 2026
Vertical standards deadline
Harmonised standards for specific product categories.
20 January 2027
Machinery Regulation: applies
Connected machines need cybersecurity evidence in the technical file for CE marking.
11 December 2027
Full application
CE marking, conformity assessment, technical documentation, SBOM, secure-by-design, security updates across the support period.
SCOPE
Manufacturers
Anyone who develops, manufactures, or has products with digital elements designed and developed under their name or trademark.
Importers
Entities established in the EU that place a product with digital elements bearing a third-country manufacturer's name on the EU market.
Distributors
Any party in the supply chain, other than the manufacturer or importer, who makes a product with digital elements available in the EU market.
MACHINERY
Applies from
Main concern
Software covered
SBOM
Where the evidence goes
CLASSIFICATION
Default (~90%)
Important Class I
Important Class II
Critical
SBOM REQUIREMENTS
REPORTING
24h
Clock starts at awareness, not confirmation
72 hrs
Initial severity assessment and mitigations
14 days
A workaround counts as a corrective measure
1 month
Runs from the 72-hour notification
Early Warning
Notification
Final report
WORTH KNOWING
Only actively exploited vulnerabilities and severe incidents are reportable. Flaws you find and fix before exploitation stay in normal vulnerability handling.
Applies to products already on the EU market, not only those placed after September 2026.
One submission through the ENISA Single Reporting Platform (Article 16) reaches both ENISA and your coordinating national CSIRT.
Microenterprises and small enterprises cannot be fined for missing the 24-hour early warning (Article 64(10)(a)). The obligation itself, and the later deadlines, still apply.
The CRA sets no deadline for developing the fix, but "without undue delay" applies and affected users must be informed under Article 14(8).
NEW • FREE RESOURCE
Minimum
Clears the CRA on paper
Audit-ready
What an auditor accepts
Depth
Top-level dependencies only
✓ Full transitive dependency tree
Cadence
Generated once, at documentation time
✓ Regenerated on every build
Vulnerability context
Not required
✓ Monitored for new vulnerabilities, with VEX
Format
A commonly used format
✓ Validated CycloneDX or SPDX (BSI TR-03183-2)

Generation
Content & Quality
Lifecycle
Vuln & VEX
Format
Integration
Beyond CRA
Get the rubric
Tell us where to send it and we’ll email it over.
PLATFORM
FAQ
What is the EU Cyber Resilience Act?
The CRA is an EU regulation establishing mandatory cybersecurity requirements for products with digital elements sold in the European Union. It covers hardware and software, requiring secure-by-design development, vulnerability handling, and ongoing security updates throughout the product lifecycle.